Testimonials
Services
Franchise - Legal Consultation
DPDPA Playbook: Legal, Tech, Board, Compliance
DPDPA Scoping Assessment
Fractional DPO / DPDPA Compliance
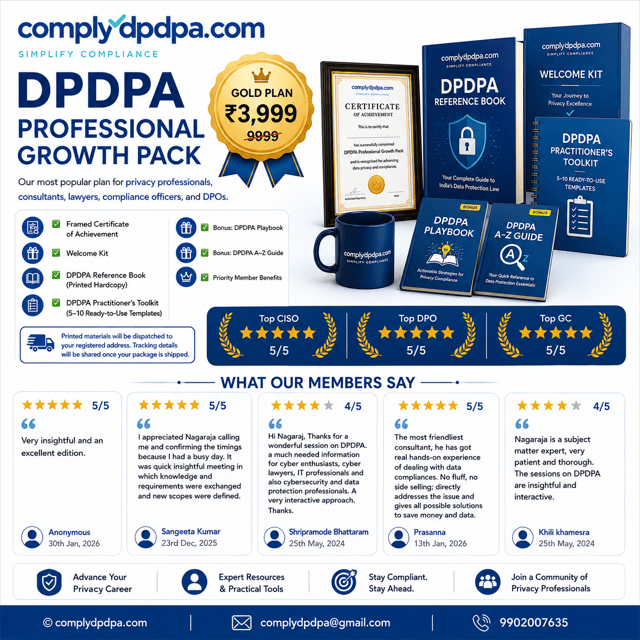
DPDPA Professional Growth Pack 🥇 Gold Plan
DPDPA Tool Evaluation & Compliance Planning
About me
- Nagaraj’s international trademark expertise is unmatched. He helped us secure our brand protection strategy across multiple markets seamlessly.Recommended by Vishal Sinha on

Frequently asked questions
What is DPDP compliance in India?
DPDP compliance means meeting the obligations under India's Digital Personal Data Protection Act, 2023 — collecting personal data with clear notice and free consent, using it only for the stated purpose, applying reasonable security safeguards, honouring data principals' rights (access, correction, erasure), reporting breaches, and resolving grievances. It applies to every data fiduciary processing digital personal data in India, including startups, BFSI, healthcare, SaaS, e-commerce and multinational companies.
How to get DPDP compliance in India?
Most organisations start with a DPDPA gap assessment, then build a data inventory and records of processing, redesign consent notices and flows, implement security safeguards and breach-response processes, set up grievance redressal, review vendor contracts, and train employees. A phased approach works best — scoping first, then fixing high-risk processing — instead of trying to do everything at once.
What should a DPDPA compliance checklist include?
A practical DPDPA compliance checklist covers lawful notice and consent capture, purpose limitation, data inventory and ROPA, security safeguards, breach notification procedure, data principal rights workflows, children's data protections, processor and vendor contracts, cross-border transfer review, published grievance officer contact details, and periodic audits plus privacy training.
What are the DPDPA compliance timelines in India?
The Act was passed in 2023, but obligations apply in phases as the government notifies the DPDP Rules, so binding timelines follow that notification schedule. In practice, companies need several months for gap assessment, consent revamp and policy updates, and once the rules are fully in force, breach reporting and grievance handling become strictly time-bound — which is why early preparation matters.
How do I choose the right DPDPA compliance tool?
Evaluate a DPDPA compliance tool against your actual gaps: consent capture and revocation, data mapping and ROPA, breach workflows, data principal request handling, vendor management and audit reporting. Make sure it supports India-specific DPDP requirements (including consent managers) and not just GDPR, integrates with your existing tech stack, and fits your sector and company size before you buy.
What do DPDPA compliance services include?
DPDPA compliance services typically include privacy gap assessments, scoping studies, data protection impact assessments, data inventory and ROPA creation, consent management framework design, policy drafting, vendor risk reviews, breach-response planning, privacy training and DPO support. Many companies also opt for fractional DPO services, which give ongoing compliance oversight without the cost of a full-time hire.
Which data privacy laws in India apply to my business?
The Digital Personal Data Protection Act, 2023 is the core statute for digital personal data, and the IT Act, 2000 with its SPDI Rules continues to govern reasonable security practices. Sectoral regulators — RBI for banks and payments, SEBI, IRDAI, and health sector rules — add further data obligations, and businesses serving EU or US users may also need to comply with GDPR or similar laws.
Do I need a data protection officer for my business in India?
Under the DPDP Act, a Data Protection Officer must be appointed if your organisation is notified as a Significant Data Fiduciary — the DPO must be an individual based in India and act as the contact point for data principals and the Data Protection Board. Even where it is not mandatory, appointing a DPO or a fractional DPO is a practical way to manage consent, breach readiness and accountability, and GDPR can separately require one if you serve EU users.
What is a data protection officer responsible for?
A data protection officer monitors the organisation's privacy compliance under the DPDP Act, advises on DPIAs and data audits, handles data principal requests and grievances, and liaises with the Data Protection Board of India. The role also involves working with legal, IT, HR, marketing and security teams to embed privacy-by-design and publishing official contact details for data principals.
How to become a data protection officer in India?
There is no single licensed route, but the strongest path combines a foundation in privacy law (DPDP Act, GDPR), working knowledge of IT and security practices, a recognised DPDPA-focused certification, and hands-on experience with gap assessments, DPIAs, consent management and breach response. Professionals from legal, compliance, audit and IT backgrounds commonly move into DPO roles in India.
Is a data protection officer certification worth it in India?
Yes — the DPDP Act does not mandate any specific qualification, but a data protection officer certification signals practical competence to employers and helps professionals from legal, IT, audit or compliance backgrounds make the switch. Any data privacy certification you pick should be updated for the DPDP Rules, India-focused, and include practical assignments rather than theory alone.
What is the data protection officer salary in India?
It varies widely with seniority, industry and company size. BFSI, IT, healthcare and consulting firms generally pay a premium, and professionals with hands-on DPDPA experience command more than general compliance roles because qualified privacy talent is still scarce. Fractional DPOs, who serve multiple companies, typically work on monthly retainers instead of salaries.
How to find a data protection officer for your company?
Decide first between a full-time in-house hire and a fractional DPO service — larger data volumes and Significant Data Fiduciary status usually justify a full-time role, while a fractional DPO gives ongoing coverage at lower cost. Look for DPDPA plus GDPR expertise, an understanding of both legal and technical controls, experience in your sector, and the ability to work with boards, IT and security teams.
What is data privacy in AI?
Data privacy in AI refers to how AI and GenAI systems collect, process and protect personal data — covering consent for training data, data minimisation, transparency about automated decisions, prevention of re-identification, and the ability to honour correction and erasure requests. In India, AI products handling personal data fall within the DPDP Act, so AI governance frameworks covering consent, data provenance and accountability are becoming essential.
What is data privacy and data security?
Data privacy is about the rights of individuals and the lawful, purpose-limited use of their personal data, while data security is the technical protection of that data through safeguards like encryption and access control. You can be secure and still not privacy-compliant — for example, by over-collecting data — and India's DPDP Act requires organisations to get both right.